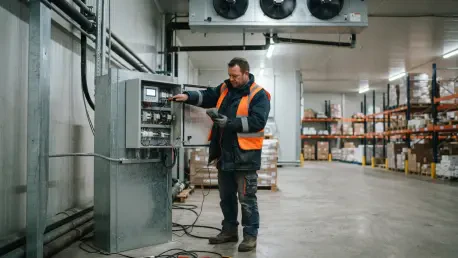
Retailers across several European nations faced tens of millions of euros in losses after attackers exploited the digital vulnerabilities of essential cold-chain infrastructure. The disruption began when sophisticated actors targeted the refrigeration controllers of major grocery chains, specifically in France and later expanding to Sweden, Belgium, and Ireland. By remotely manipulating the defrost settings, these attackers triggered a thermal surge that reached temperatures of 50°C (122°F), effectively destroying massive quantities of perishable food items and even causing physical fires in some distribution centers. This incident serves as a grim reminder that the boundary between digital security and physical safety has largely evaporated in the modern industrial landscape. As enterprises integrate thousands of smart sensors into their daily operations, the potential for catastrophic failure increases significantly. The cold-chain crisis was not a localized glitch but a deliberate exploitation of nontraditional IT assets.
Identifying Risks and Implementing Zero-Trust Solutions
Risks: Unsecured IoT Growth
The rapid expansion of the Internet of Things has outpaced the security protocols necessary to protect it, leaving countless industrial systems exposed to external interference. Many commercial devices, such as HVAC units and specialized refrigeration sensors, are frequently manufactured with a focus on cost and connectivity rather than defensive robustness. Unlike a standard laptop or corporate server, these tools often lack the processing power to run sophisticated encryption or antivirus software, creating a permanent soft spot in the network perimeter. As companies scale their digital footprints from 2026 to 2028, the volume of these vulnerable endpoints continues to climb, providing attackers with an ever-expanding library of entry points. When these devices are deployed without rigorous oversight, they often bypass traditional firewalls entirely, allowing malicious actors to gain a foothold in a secondary system before moving into the core corporate data environment.
Furthermore, the lack of standardized security updates for legacy IoT hardware creates a significant risk for many industrial operations that rely on older machinery. Many of the refrigeration controllers involved in the recent European crisis were running on firmware that had not been updated for years, making them easy targets for known exploit kits found on the dark web. This vulnerability is compounded by the fact that many of these devices are installed by third-party contractors who may prioritize functionality over security settings. Consequently, default passwords and unencrypted communication ports remain active long after the initial installation, inviting unauthorized access from anyone with basic scanning tools. This systemic failure to treat IoT hardware as a critical security asset has fundamentally shifted the risk profile for modern retailers. It is no longer sufficient to secure the front door of the data center while leaving the back windows of the infrastructure completely open.
Frameworks: The Shift to Zero-Trust
To counter these pervasive threats, the industry is increasingly turning toward a zero-trust architecture that fundamentally changes how network traffic is authorized and managed. Ericsson’s NetCloud Secure Connect is at the forefront of this movement, replacing traditional security methods that often rely on a trusted perimeter that can be easily breached. In a zero-trust environment, no device is implicitly trusted, regardless of whether it is located inside or outside the corporate office. Every connection request must be verified and authenticated before access is granted to any specific resource. This approach utilizes resource cloaking, which effectively hides IoT devices from the public internet by making them invisible to unauthorized scanners. By ensuring that these controllers do not possess a public-facing IP address, organizations can drastically reduce their attack surface. This architectural shift represents a proactive defense strategy that prioritizes the containment of threats.
Building on this foundation, the zero-trust model emphasizes the prevention of lateral movement, which is the primary method used by attackers to escalate a minor breach into a total system failure. By implementing strict micro-segmentation, a network can isolate a compromised device, such as a single fridge controller, and prevent it from communicating with sensitive servers or financial databases. This “deny-all-by-default” logic ensures that traffic only flows between pre-approved endpoints that have a legitimate business need to interact. In the event of a breach like the one seen in the European cold-chain attacks, such a system would have limited the damage to a single unit rather than allowing the infection to spread across an entire national fleet. Moreover, this framework provides IT teams with granular visibility into every packet of data moving across the network, enabling them to detect and mitigate anomalous behavior in real time before it impacts the business.
Connectivity: Advanced Hardware and Orchestration
Implementing a high-level security strategy requires specialized hardware that can maintain resilient connections even in the harshest industrial or commercial environments. The Ericsson Cradlepoint S400 has emerged as a cornerstone for this transition, providing a semi-ruggedized 5G router specifically engineered for IoT applications. Unlike consumer-grade networking equipment, this device is built to withstand temperature fluctuations and physical vibrations common in warehouses or manufacturing floors. It supports a wide range of interfaces, including serial ports and general-purpose input/output connections, allowing it to bridge the gap between legacy industrial machinery and modern high-speed networks. By integrating these robust routers at the network edge, enterprises can establish secure, encrypted tunnels for all their sensor data, ensuring that sensitive operational information remains protected from interception. This hardware-centric approach provides the foundation for advanced security.
Managing thousands of distributed devices across multiple geographical locations is a monumental task that requires a sophisticated, centralized orchestration platform. Tools like NetCloud Manager provide IT teams with a comprehensive view of their entire IoT ecosystem, allowing them to push security policies and firmware updates to every device simultaneously. This centralized approach eliminates the need for manual, on-site intervention, which is often too slow and expensive to be effective during a crisis. When a new vulnerability is discovered, a security patch can be deployed across the global fleet in minutes, effectively closing the door on potential attackers before they can exploit the weakness. This level of agility is a critical differentiator for companies looking to protect themselves against the rapid evolution of modern cyber threats. By automating the lifecycle management of their hardware, enterprises ensure that every sensor and controller remains compliant.
Strategic Recommendations for Future Resilience
Organizations that successfully navigated the aftermath of the cold-chain crisis recognized that reactive security was no longer a viable strategy for the digital age. They moved away from the outdated concept of a hard perimeter and instead embraced a decentralized, zero-trust model that protected every individual asset. By prioritizing the deployment of ruggedized 5G hardware and AI-driven management platforms, these enterprises effectively neutralized the vulnerabilities that attackers once exploited with such ease. The decision to audit every connected sensor and isolate legacy hardware proved to be a critical turning point in preserving both operational uptime and financial stability. These leaders did not wait for the next wave of attacks to refine their defenses; they proactively transformed their IoT infrastructure into a resilient foundation for growth. As a result, the physical safety of their facilities and the integrity of their supply chains were solidified against the growing threat of digital sabotage.