Automated malware blocking and real-time process termination are essential components for protecting Linux cloud environments from chained vulnerabilities. As digital transformation reaches its peak in 2026, the friction between high-velocity software delivery and robust security has never been more apparent. Engineering teams frequently prioritize application uptime and low latency above all else, often viewing security instrumentation as an unnecessary evil that introduces unwanted overhead. This tension is particularly acute within Kubernetes clusters where ephemeral workloads demand instantaneous scaling. When traditional security tools consume excessive CPU cycles, the immediate response from DevOps is often to disable them, leaving critical infrastructure exposed. The emergence of the Cortex Cloud Sensor by Palo Alto Networks represents a strategic pivot in this landscape, designed to offer a lightweight footprint while maintaining the aggressive defensive posture required to stop modern exploits in their tracks during runtime.
The Urgency: Combating Rapid Threat Cycles in 2026
The threat landscape has shifted significantly, with attackers now employing sophisticated artificial intelligence to automate the discovery of vulnerabilities. Data from specialized incident response teams suggests that the window between initial access and data exfiltration has plummeted to less than 72 minutes, reflecting a massive increase in speed compared to recent years. This hyper-accelerated timeline renders manual intervention and even standard alert-based systems largely ineffective. By the time a security analyst receives a notification and begins an investigation, the adversary has often already completed their mission and vanished. This reality necessitates a transition toward autonomous security systems that can act at the speed of the attack itself. The Cortex Cloud Sensor is engineered to function as an active participant in the environment, capable of identifying and neutralizing threats without waiting for external confirmation, thereby closing the dangerous gap created by human latency in high-stakes environments.
This shift toward proactive defense is not just about speed; it is about the complexity of the attacks being mitigated. Chained vulnerabilities, where multiple minor flaws are combined to achieve a devastating breach, have become the standard methodology for sophisticated state-sponsored groups and organized cybercriminals. These attacks often occur in the volatile space of runtime memory, making them invisible to static scanning tools that only look at code before it is executed. To counter this, the sensor remains vigilant throughout the entire lifecycle of a container, monitoring for the subtle signs of process injection or unauthorized privilege escalation. By enforcing strict security policies at the kernel level, the system ensures that any deviation from normal behavior is met with an immediate lockdown. This level of granular control is vital for organizations that cannot afford even a single second of exposure, providing a layer of protection that evolves as quickly as the threats it faces in the cloud.
Security Models: Overcoming Performance Bottlenecks
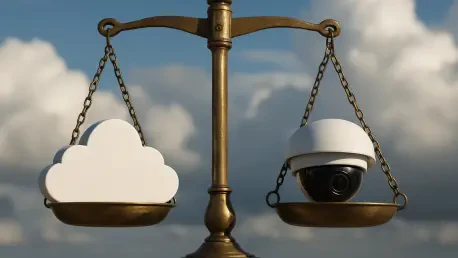
For years, organizations have been forced to navigate a binary choice between agentless scanning and traditional security agents. Agentless methods are favored for their zero impact on performance, providing a clear map of vulnerabilities and misconfigurations without touching the live workload. However, while these tools are excellent for visibility, they lack the operational power to stop an active breach once it begins. Conversely, legacy security agents provide runtime protection but often come with a heavy resource tax, consuming significant amounts of memory and CPU power that could otherwise be used to serve end users. In high-density container environments, this overhead translates directly into higher cloud bills and slower application response times. The Cortex Cloud Sensor seeks to break this compromise by utilizing a hybrid approach. It offloads the resource-intensive tasks of deep file scanning to an agentless backend while keeping the active defense mechanism on the host as slim and efficient as possible for real-time monitoring.
This strategic division of labor ensures that the most critical workloads remain protected without the operational friction that typically arises between security and development teams. By reducing the overall footprint of the sensor, companies can maintain the high performance required for their customer-facing applications while still benefiting from a robust security posture. This is especially important as businesses expand their use of microservices, where dozens of small containers might run on a single host. If each of those containers required a heavy security agent, the host would quickly become overloaded. The Cortex Cloud Sensor addresses this scalability challenge by providing a unified, lightweight framework that protects all containers on a node simultaneously. This approach allows enterprises to scale their cloud footprint horizontally without fear that their security costs or latency will spiral out of control, effectively aligning security objectives with the core goals of modern infrastructure management.
Technical Innovation: The eBPF and AI Advantage
At the heart of this new architectural efficiency is the integration of eBPF technology, which allows the sensor to run sandboxed programs within the Linux kernel. Historically, security agents relied on kernel modules that could cause system instability or crashes during version upgrades. By using eBPF, the Cortex Cloud Sensor can observe system calls and network traffic with minimal overhead and without the risk of compromising the underlying operating system stability. This ensures that kernel updates do not lead to application downtime, a major pain point for site reliability engineers who manage large-scale fleets. The sensor uses up to 75% fewer resources than its predecessors by focusing strictly on the events that matter most during runtime. This lean design is particularly beneficial for ephemeral environments where containers may only exist for seconds or minutes. The sensor is ready to defend these workloads the moment they are instantiated, providing immediate coverage that matches the dynamic nature of the cloud.
Achieving a balance between security and performance required a departure from the monolithic security models of the past. Organizations that adopted the Cortex Cloud Sensor successfully integrated active runtime protection into their continuous delivery pipelines, ensuring that safety was never treated as an afterthought. This transition allowed engineering teams to maintain high-velocity deployments while the security apparatus operated silently in the background, neutralizing threats through automated intervention and behavioral analysis. Looking forward, enterprises should consider standardizing these lightweight, kernel-level protections across all containerized environments to eliminate visibility gaps. The path to a secure cloud landscape involved the adoption of technologies like eBPF and AI-driven telemetry, which proved that protection could be both aggressive and efficient. By prioritizing this balance, businesses were able to innovate at scale, confident that their most critical assets were shielded from the evolving tactics of modern adversaries.