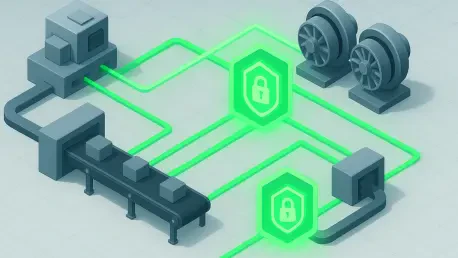
Unlike standard IT settings where devices fail-closed, industrial firewalls must be configured with specific failure modes to ensure process continuity and worker safety. Historically, factory floors operated under the protective umbrella of physical isolation, utilizing proprietary communication protocols that were functionally invisible to the outside world. This era of security through obscurity has rapidly dissolved as the Fourth Industrial Revolution mandates a seamless exchange of data between the shop floor and the corporate boardroom. Today, the convergence of operational technology and information technology allows for unprecedented levels of production transparency and remote maintenance. However, this same connectivity exposes critical infrastructure, such as Programmable Logic Controllers, to digital threats that were once confined to office networks. To mitigate these risks, industrial firewalls have emerged as the primary defense, providing specialized gatekeeping that standard office hardware cannot perform in high-stakes environments.
Bridging the Gap Between IT and OT Networks
Strategic Integration: Protocol Intelligence and Deep Packet Inspection
Standard enterprise firewalls are typically designed to filter high-volume web traffic and basic file transfers, yet they remain fundamentally blind to the specialized languages used by factory machines. In contrast, industrial firewalls leverage Deep Packet Inspection engines capable of understanding the semantic nuance within protocols like Modbus, DNP3, and OPC-UA. Instead of merely blocking or allowing traffic based on source and destination addresses, these advanced devices can analyze the specific intent of a command packet. For instance, a firewall might permit a status request from a Human-Machine Interface but instantly block a command to modify a safety threshold or stop a turbine if that instruction originates from an unauthorized zone. This level of granular control is essential because it allows the manufacturing process to continue without interruption while simultaneously filtering out malformed instructions that could lead to equipment failure or catastrophic physical accidents.
The integration of these intelligent filtering systems allows organizations to maintain a cohesive security posture without sacrificing the benefits of real-time data flow. By interpreting the specialized instructions sent to industrial controllers, these firewalls provide a layer of visibility that was previously non-existent in legacy environments. Modern production cycles often rely on high-level analytics and predictive maintenance models that require constant communication with cloud-based platforms or off-site engineering teams. Without protocol-aware firewalls, these connections would represent a massive vulnerability, as a single compromised gateway could provide a pathway for attackers to manipulate physical hardware directly. Consequently, the deployment of industrial firewalls represents a shift from reactive security to proactive process protection, ensuring that every piece of data entering the operational network is scrutinized for both safety and authorization before it reaches its destination.
Hardened Hardware: Real-Time Operational Resilience and Timing
Beyond the sophisticated software layer, the physical architecture of industrial firewalls is specifically engineered to withstand the brutal environmental conditions common to factory floors and remote utility sites. Traditional office-grade appliances are designed for climate-controlled server rooms and would quickly succumb to the extreme temperatures, high humidity, and pervasive airborne dust found in heavy manufacturing. Industrial firewalls are often encased in ruggedized, fanless chassis that dissipate heat efficiently while providing protection against electromagnetic interference and mechanical vibrations. This hardware resilience ensures that security measures do not become a point of failure themselves, maintaining continuous uptime in environments where a hardware crash could stop an entire assembly line. For many facilities, the ability of these devices to operate reliably in sub-zero or scorching temperatures is just as critical as their digital defense capabilities, as environmental failure is a common cause of downtime.
Operationally, these devices are optimized for near-zero latency, which is a non-negotiable requirement for real-time control systems. In a standard IT environment, a delay of a few milliseconds in packet delivery is often unnoticeable, but in a safety-critical industrial process, such a delay can be disastrous. High-speed robotics and synchronized conveyor systems rely on precise timing to function safely; even a minor desynchronization caused by a sluggish firewall can lead to physical collisions, damaged products, or mechanical strain. Industrial firewalls utilize hardware-accelerated processing to ensure that security inspection does not introduce significant lag into the communication loop. This performance-first approach allows security teams to implement rigorous inspection policies without throttling the speed of production, effectively balancing the need for deep technical oversight with the demanding requirements of high-volume, automated manufacturing cycles that run around the clock.
Architectural Frameworks and Sector Applications
Segmented Environments: Implementing the Purdue Model and Safety
A core strategy for securing modern manufacturing involves the implementation of the Purdue Reference Model, which organizes industrial networks into hierarchical levels or zones. This architectural framework creates clear boundaries between business-oriented enterprise networks and the safety-critical components of the control layer. Industrial firewalls serve as the essential conduits between these zones, regulating the flow of information and preventing unauthorized lateral movement. If a breach occurs within the corporate office, the firewalls at the zone boundaries ensure that the infection cannot spread to the supervisory control or basic automation layers. This segmentation is vital for isolating sensitive equipment from the inherently less secure Internet of Things devices that are increasingly common in modern offices. By establishing these strictly controlled pathways, organizations can limit the blast radius of any individual cyber incident and ensure that critical processes remain isolated from external threats.
The practical application of this zoning strategy allows for a defense-in-depth approach where multiple layers of security must be breached before an attacker can reach the most sensitive parts of the facility. Each zone can be governed by its own set of security policies tailored to the specific functions of the equipment residing within it. For example, the zone containing robotic welding units might have extremely restricted communication rules compared to the zone handling shipping and logistics data. This granular segmentation not only enhances security but also simplifies troubleshooting and maintenance, as network traffic is compartmentalized into logical groups. Furthermore, the use of industrial firewalls at these boundaries provides an audit trail for all inter-zone communications, giving security professionals the ability to identify anomalies in real time. This structural discipline is what allows complex, interconnected factories to operate with the same level of confidence as the air-gapped systems of the past.
Industry-Specific Security: Protecting Critical Infrastructure and Quality
The necessity of industrial firewalls is particularly evident in the automotive sector, where highly automated assembly lines operate on razor-thin margins. A single minute of unplanned downtime in a robotic painting or welding cell can cost tens of thousands of dollars in lost production and wasted materials. In these environments, firewalls protect the synchronized dance of thousands of sensors and actuators, preventing external interference from disrupting the precise timing required for vehicle assembly. Similarly, in public infrastructure projects like water treatment, firewalls serve as a critical defense for SCADA systems that monitor chemical levels and distribution pumps. As these facilities move toward remote monitoring and cloud-based diagnostics, the firewall ensures that only authorized personnel can access control interfaces. By shielding these vital services from malicious actors, industrial firewalls play a central role in maintaining public safety and the reliable operation of the essential infrastructure.
The transition toward a fully digitized industrial landscape necessitated a fundamental rethink of how physical assets were protected from virtual threats. Organizations that successfully navigated this shift focused on deploying purpose-built firewalls that recognized the unique operational demands of the factory floor. These technical leaders prioritized the implementation of deep packet inspection and network segmentation as the cornerstones of their defense strategy. By moving away from the outdated concept of air-gapped security, manufacturers embraced a more robust, active model of protection that emphasized physical safety alongside data integrity. The adoption of these specialized gatekeepers provided a blueprint for securing the production environment, allowing for the safe integration of advanced analytics and remote diagnostics. As manufacturing environments became increasingly complex, the role of the industrial firewall was solidified as a definitive barrier. Moving forward, the most effective strategies involved continuous protocol updates and the integration of automated threat response systems.