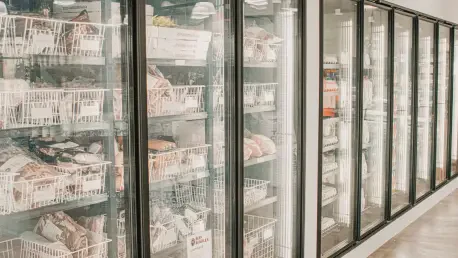
Local trade associations in Cyprus are urging supermarket chains to reassess their digital infrastructure as larger retailers adopt increasingly sophisticated management software. The modern threat landscape has shifted dramatically, moving beyond the traditional confines of personal computers and mobile devices to target the essential hardware that sustains daily commerce. Recent reports from across Europe have detailed alarming instances where hackers successfully infiltrated refrigeration control systems, causing widespread temperature fluctuations that led to significant inventory spoilage. These digital incursions do not merely compromise data; they disrupt the physical supply chain and result in substantial financial losses for retailers who rely on internet-connected sensors to maintain food safety standards and operational efficiency.
While authorities in Cyprus have not yet officially recorded specific complaints regarding these refrigeration breaches, the increasing reliance on remote-management software makes the local sector a prime target for future exploitation. Larger supermarket chains often operate advanced infrastructures that provide multiple entry points for malicious actors if not properly secured. The digital resilience of these systems is no longer a luxury but a fundamental requirement for business continuity. Security experts emphasize that protection involves more than just perimeter defense; it requires a proactive approach to detecting and limiting the impact of an intrusion to ensure that critical services, such as the cold chain, remain operational even during a coordinated cyber campaign.
1. Step 1: Fortify Your Household Wireless Network
The home router serves as the primary gateway for every connected device, making it the most critical point of failure in a residential digital environment. To establish a secure foundation, users must implement a robust and unique password that avoids common dictionary words or easily guessable personal information. This primary credential should be entirely different from the one used to access the router’s administrative settings, which controls the underlying configuration of the entire network. Without these distinct layers of protection, an intruder who compromises a single connected appliance could potentially gain full control over the central networking hardware, leading to a complete breach of privacy.
In addition to strong passwords, the technical standards used for encryption play a vital role in keeping unauthorized users out of the wireless signal. Modern routers offer WPA3 encryption, which provides significantly better protection against brute-force attacks compared to older protocols. If a device or router does not support WPA3, the next best option is WPA2, but older standards like WEP should be strictly avoided as they are easily bypassed by even novice hackers. By ensuring the highest available encryption is active, residents can create a much more difficult environment for external actors to intercept data or inject malicious code into the various smart devices operating within the home.
2. Step 2: Update Factory-Set Login Credentials
Many smart home products and commercial sensors arrive from the manufacturer with standard, default login details that are publicly available in online databases. These factory-set passwords represent one of the most common vulnerabilities exploited by automated bots scanning the internet for accessible hardware. It is essential to update these credentials immediately upon the first installation of any new device, whether it is a security camera, a smart thermostat, or a commercial cooling controller. Using a unique set of login details for every single piece of equipment ensures that a vulnerability in one product does not provide a skeleton key to the rest of the ecosystem.
The practice of password reuse remains a significant risk factor in both residential and commercial sectors. If an attacker discovers the password for a relatively low-security device, such as a smart plug, they will often attempt to use those same credentials to access more sensitive systems like email accounts or financial portals. Diversifying authentication details across all services and hardware creates a compartmentalized security structure where a single compromised point remains isolated. This strategy significantly limits the potential for lateral movement within a network, preventing a minor localized incident from escalating into a full-scale digital disaster that threatens personal data and physical safety.
3. Step 3: Activate Multi-Layered Verification
Implementing two-factor or multi-factor authentication provides a critical secondary defense that can stop an attack even if a primary password has been stolen. This additional layer typically requires a time-sensitive code sent to a mobile device or generated by a dedicated application, ensuring that only the authorized user can finalize a login attempt. Most modern cloud services that manage smart home devices now offer this feature, yet many consumers neglect to enable it. Activating this verification process transforms a single-point failure into a much more complex hurdle for hackers, as they would need simultaneous access to both the password and the physical secondary device.
The effectiveness of multi-layered verification is particularly evident during credential stuffing attacks, where hackers use lists of leaked passwords to gain unauthorized access to accounts. Even if the correct username and password are provided, the system will block the entry until the second factor is verified. This serves as an early warning system, as the legitimate owner will receive a notification of a login attempt they did not initiate, allowing them to change their compromised password before any damage occurs. In an era where digital identities are constantly under threat, this simple configuration step represents one of the most effective ways to secure internet-linked hardware against remote intrusion.
4. Step 4: Install System Patches Promptly
Software updates are frequently misunderstood as mere feature additions, but they often contain vital security patches designed to close newly discovered vulnerabilities. When manufacturers identify a flaw that could allow unauthorized access, they release firmware updates to fix the problem before it can be widely exploited. Dismissing these update notifications leaves devices exposed to known threats that hackers can easily target using automated tools. To maintain a strong defensive posture, users should ensure that smartphones, computers, smart televisions, and all internet-connected appliances are consistently running the latest software versions provided by the developer.
The most efficient method for staying current with these critical fixes is to enable automatic updates whenever the option is available. This reduces the burden on the user to manually check for patches and ensures that protection is applied as soon as it becomes available. In a commercial setting, such as a supermarket with hundreds of connected sensors, automated patch management is even more crucial for preventing a single unpatched controller from becoming the entry point for a network-wide breach. Proactive maintenance of digital systems is a continuous process that requires vigilance to stay ahead of the evolving tactics used by modern cybercriminals.
5. Step 5: Restrict Off-Site Control Features
While the ability to manage household appliances or commercial systems from a remote location offers significant convenience, it also creates an external pathway that can be exploited by malicious actors. Many users do not actually require the capability to adjust their thermostats or view camera feeds while away from home, yet these features are often enabled by default. Disabling remote-access functions when they are not strictly necessary significantly reduces the attack surface of a device. By restricting control to the local network only, a user ensures that an attacker would need to be physically within range of the Wi-Fi signal to attempt an intrusion.
A similar principle of restriction should be applied to the networking hardware itself, specifically the administrative interfaces of routers and switches. Unnecessary management features, such as remote web administration or Universal Plug and Play, should be deactivated to prevent external scans from identifying open ports. Limiting the ways in which a system can be reached from the public internet is a fundamental tenet of digital security. This cautious approach forces any potential attacker to work much harder to find a viable entry point, often encouraging them to move on to easier, less protected targets that leave their remote doors wide open for exploitation.
6. Step 6: Establish a Dedicated Network for Smart Hardware
Segmenting a home or business network is a highly effective way to isolate potential threats and protect sensitive information from vulnerable IoT devices. Many modern routers allow for the creation of guest networks or secondary SSIDs, which can be used to host smart cameras, plugs, and appliances separately from the main computers used for banking or private work. This network isolation ensures that if a smart light bulb is compromised, the attacker is confined to that specific segment and cannot easily bridge over to the primary network where more valuable personal data is stored.
This architectural approach to security mimics the professional standards used in high-security commercial environments. By keeping “chatty” or less secure IoT devices on a dedicated VLAN, users prevent these products from communicating with other hardware on the network. This significantly limits the risk of data exfiltration and prevents malicious code from spreading between different classes of devices. As the number of connected gadgets in the average household continues to grow, network segmentation provides a scalable way to manage the inherent risks of the Internet of Things without sacrificing the convenience that these modern technologies provide to the end user.
7. Step 7 and 8: Audit Your Programs and Purchasing Safely
Stakeholders recognized that digital safety began long before a device was even plugged into a wall. By auditing software permissions and researching manufacturer support cycles, proactive users established a resilient perimeter against the rising tide of IoT exploitation. They learned that downloading applications only from reputable sources and closely monitoring the data access requested by those programs prevented many common privacy breaches. This historical shift toward digital literacy meant that consumers became more selective, favoring brands that demonstrated a commitment to long-term security updates over those that offered cheaper, unsupported hardware that quickly became obsolete.
The conclusion of this period of technological transition highlighted the importance of viewing cybersecurity as a continuous lifecycle rather than a one-time setup. It was understood that a device remaining functional did not necessarily mean it remained secure, especially after the manufacturer ceased providing critical safety patches. By evaluating the digital track record of a company before making a purchase, businesses and individuals alike avoided the pitfalls of legacy hardware. These collective efforts to audit existing systems and prioritize supported technology effectively mitigated the risks posed by the complex web of connected devices that defined the modern era of the internet.