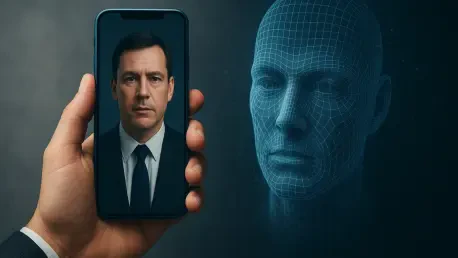
Gartner reports that by late 2025, more than sixty percent of organizations had already experienced some form of deepfake attack involving social engineering or automated process exploitation. This startling figure highlights a fundamental shift in the cyber-threat landscape, where the biological hallmarks of identity—voices, faces, and mannerisms—are no longer reliable indicators of authenticity. As generative artificial intelligence reaches a state of near-perfection, the corporate world finds itself grappling with a reality where a video call from a Chief Financial Officer might be nothing more than a highly sophisticated digital puppet. This technological maturation has forced Chief Information Security Officers to rethink their entire defensive architecture, moving from traditional network-centric security toward a model that prioritizes identity protection. The challenge lies in the fact that these synthetic threats bypass conventional firewalls by targeting the inherent human trust that underpins every business interaction.
Quantifying the Surge: Synthetic Identity Theft
Recent data from global security analysts indicates that the frequency of these attacks is not just growing but accelerating at a pace that traditional defense mechanisms struggle to match. Between 2024 and 2026, the instances of high-fidelity video impersonation have nearly doubled, while audio-based voice cloning has become a standard tool in the fraudster’s arsenal. The financial stakes have risen accordingly, with recent incidents involving major banking institutions resulting in losses exceeding one hundred million dollars. These are no longer isolated experiments by fringe hackers but coordinated campaigns by well-funded criminal enterprises that treat deepfake technology as a scalable business model. The shift suggests that any organization with a public-facing leadership team is a potential target, as the vast amount of media available online provides the training set for creating convincing clones. This pervasive exposure has rendered standard security training obsolete for most firms.
The psychological foundation of these attacks relies on what experts call the weaponization of trust, a tactic that exploits the cognitive shortcuts humans use to verify identity. When an employee sees a familiar face on a screen or hears a recognizable voice on the phone, their critical thinking often yields to the authority of the perceived individual. Fraudsters capitalize on this by creating high-pressure scenarios, such as urgent wire transfers or sensitive data requests, where the victim is discouraged from questioning the source. This dynamic creates a significant paradox for modern executives who must balance the need for public visibility with the risk of providing attack infrastructure for AI training. Every keynote speech, podcast interview, and social media video contributes to a library of data that criminals can use to replicate an executive’s persona. Consequently, the damage extends beyond immediate financial loss to include a lingering sense of operational friction.
Strategic Mitigation: Technical and Operational Defense
Since preventing the generation of synthetic media is effectively impossible in a globalized digital environment, security leaders are refocusing their efforts on containing the potential impact through operational resilience. Moving beyond generic warnings, many organizations have implemented immersive scenario-based training that puts employees in high-stakes simulations involving deepfake interactions. These exercises are designed to induce the cognitive dissonance that occurs when a familiar person makes an atypical request, thereby building the muscle memory necessary for skepticism. By experiencing a simulated attack, employees learn to recognize the subtle artifacts or unusual patterns that might betray a synthetic clone, such as unnatural eye movements or slight delays in audio response. This hands-on approach transforms the human element from a primary vulnerability into a sophisticated line of defense, ensuring that staff are psychologically prepared for the reality of AI-driven fraud.
A cornerstone of this defensive evolution is the institutionalization of Out-of-Band verification protocols, which serve as a mandatory circuit breaker for high-value transactions. In this framework, any request for a significant financial move or the disclosure of sensitive credentials must be confirmed through a secondary, pre-arranged communication channel that is independent of the initial contact method. If an executive initiates a request via a video conference call, the recipient is required to verify that request through an encrypted messaging app or a direct phone call to a known, verified number. This dual-path requirement ensures that even the most convincing visual and auditory impersonation cannot succeed in isolation. By making these protocols a non-negotiable part of the corporate culture, companies create a structural barrier that is exceptionally difficult for fraudsters to bypass, regardless of how advanced their generative AI tools may be in creating convincing digital replicas.
Control Frameworks: Strengthening Financial and Detection Capabilities
To further mitigate the risks posed by synthetic identity theft, enterprises are overhauling their internal financial controls to eliminate any single points of failure that a deepfake could exploit. The implementation of rigid multi-party authorization frameworks ensures that no single individual, regardless of their seniority or the apparent urgency of the request, can authorize a substantial transfer of funds alone. This approach necessitates that multiple departments or authorized personnel sign off on a transaction, requiring a fraudster to successfully deceive several different targets simultaneously across different communication platforms. Such a requirement significantly lowers the probability of a successful heist, as the coordination required to mimic multiple stakeholders is vastly more complex than targeting a single employee. This shift toward collective responsibility moves the burden of security away from individual judgment and into a standardized, process-driven environment.
Complementing these structural controls is the deployment of proactive external monitoring systems designed to identify and neutralize impersonation attempts before they can be used in an active campaign. Advanced security stacks now often include tools that scan the deep web and social media platforms for rogue digital assets, such as cloned voices or unauthorized video avatars of company leadership. While the technology for detecting synthetic media is in a perpetual arms race with generative AI, early identification of a potential threat allows the security team to alert relevant employees and update their defensive posture before an attack is launched. This proactive stance is essential for reducing the window of opportunity for criminals. When combined with multi-layered approval processes and strict verification mandates, these detection capabilities form a comprehensive shield that protects an organization’s financial integrity and its reputation from the growing threat of synthetic deception.
Crisis Management: Navigating Legal and Reputational Risks
The aftermath of a deepfake incident presents a complex web of legal and reputational challenges that require a unified response from security, legal, and communications departments. Legal professionals emphasize that these attacks often touch upon intricate issues regarding the right of publicity, copyright infringement, and defamation, yet the reactive nature of digital privacy laws means that corporations cannot rely solely on the legal system for protection. Instead, organizations must be prepared to use existing legal frameworks to preserve forensic evidence, manage the notification of affected stakeholders, and work aggressively with platform providers to remove fraudulent content. Because the visibility of a C-suite executive is a valuable corporate asset, protecting that likeness is increasingly viewed as a legal necessity rather than just a technical problem. A siloed approach to these crises is no longer viable, as the legal and brand implications of a synthetic impersonation can last far longer.
In looking back at the rapid escalation of synthetic fraud, it became evident that the most successful organizations were those that transitioned from a culture of implicit trust to one of verified authenticity. Leadership teams recognized that while the technology behind deepfakes was revolutionary, the solution remained grounded in the fundamentals of disciplined communication and rigorous process control. The actionable next steps for any enterprise involved the immediate auditing of existing verification procedures and the adoption of decentralized approval workflows that removed the vulnerability of individual decision-making. Future considerations included the development of proprietary digital watermarks or cryptographic signatures for internal communications to ensure that every message from an executive carried a verifiable mark of origin. By fostering an institutional environment where skepticism was seen as a virtue, these companies managed to navigate the blurred lines of the digital age, effectively safeguarding their assets.