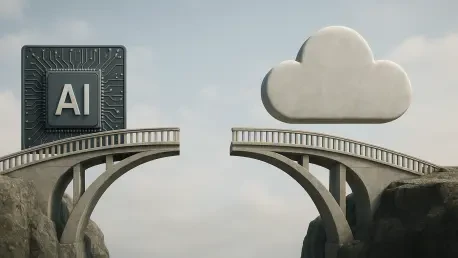
Organizations are discovering that deep visibility into cloud infrastructure is insufficient when endpoint activity remains disconnected from the broader security narrative. For years, the industry operated under the assumption that securing the cloud environment was the ultimate goal, focusing heavily on workloads and infrastructure. However, the rapid proliferation of artificial intelligence in software development has fundamentally altered the threat landscape. Developers are no longer just writing code; they are orchestrating complex AI agents that bridge the gap between local workstations and sensitive cloud assets. This shift has created a situation where a single prompt on a laptop can trigger a cascade of actions across an entire enterprise network. As these tools become more autonomous, the traditional boundaries that once separated the local device from the remote server have effectively vanished, leaving security teams struggling to maintain control over a perimeter that is now fluid and decentralized.
The Evolution of Cloud Vulnerabilities
The Developer Workstation: A New Gateway to Infrastructure
The emergence of the Model Context Protocol (MCP) has introduced a sophisticated layer of connectivity that allows AI systems to retrieve data and execute actions across multiple platforms seamlessly. In this current environment of 2026, the developer’s workstation has transformed into a powerful gateway capable of influencing enterprise-wide resources with minimal manual intervention. When a developer utilizes an AI assistant to refactor code or manage cloud deployments, the workstation acts as the command center for these operations. If an AI agent has the permissions to access a database or modify a security group, the security of that action is only as strong as the security of the local machine where the prompt originated. This creates a critical risk point where a compromise on a single endpoint can escalate into a full-scale cloud breach. The complexity of these interactions means that traditional endpoint detection systems often miss the cloud implications, while cloud security tools fail to see the local origin of the activity.
Closing the Visibility Gap Between Siloed Environments
Most modern organizations currently treat endpoint monitoring and cloud security as distinct silos, which creates a significant gap in their defensive posture. While a security operations center might have granular data on every API call within their cloud environment, they frequently lack the capability to trace those actions back to the specific user session or AI interaction on a local workstation. This lack of correlation makes it nearly impossible to distinguish between a legitimate automated process and a malicious actor leveraging an AI agent. Upwind’s latest innovations address this specific challenge by monitoring MCP connections and correlating endpoint activity with cloud identity and action logs. By bridging these two domains, organizations can finally see the complete picture of how an action initiated on a laptop moves through various stages of authentication and execution. This unified visibility is essential for detecting anomalies that would otherwise remain hidden within the noise of standard operational traffic across the infrastructure.
Unified Visibility and Contextual Security
Transitioning From Location to Context: The Security Journey
The industry is witnessing a significant transition from location-based security to context-based security, where the focus shifts from protecting a specific place to understanding the journey of an action. In the past, securing a database or a server was considered a static task centered on firewall rules and access lists. However, in the era of autonomous AI agents, security must instead prioritize the narrative of each transaction. Because these agents often operate with delegated permissions, they can act on behalf of highly privileged users, making it critical to understand what triggered a particular command. Contextual security involves analyzing the intent behind a prompt, the identity of the person initiating it, and the specific path the command took through the network. This approach allows security teams to identify suspicious behavior based on deviations from normal patterns, such as an AI agent suddenly requesting access to sensitive data that falls outside its typical scope of work or the user’s role.
Securing the Autonomous Future: Actionable Integration Strategies
Ultimately, the adoption of specialized sensors for AI endpoints provided the necessary visibility to mitigate these emerging risks. By following the full path of AI activity from the initial prompt to the final execution in the cloud, organizations established a more resilient defense against sophisticated threats. Security leaders recognized that the workstation was no longer a peripheral device but a core component of the cloud perimeter. To maintain this level of protection, teams implemented rigorous monitoring of all AI-to-cloud interactions and prioritized the integration of disparate security signals into a single, cohesive narrative. This shift toward total visibility ensured that investigations started where the activity began rather than where the damage was first detected. Moving forward, the focus remained on continuous refinement of these correlation techniques to stay ahead of the evolving capabilities of autonomous systems. These proactive measures transformed security from a reactive barrier into a strategic enabler of safe, AI-driven development.